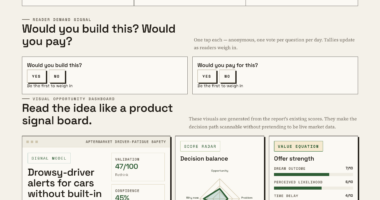
📊 Full opportunity report: Strategies For Protecting Remote Team Devices Across Different Hardware on IdeaNavigator AI — validation score, market gap, and execution plan.
Get ready for Prime Big Deal Days — try Prime free
Exclusive member deals on October 6–7, plus fast free delivery. Cancel anytime.
Start your free trialAs an affiliate, we earn on qualifying purchases.
TL;DR
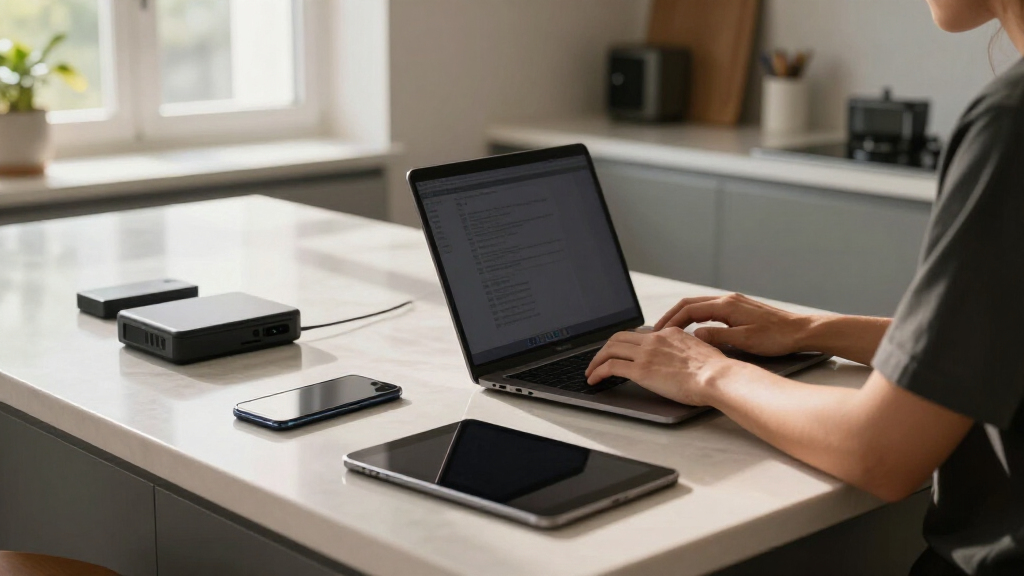
A new approach involves deploying a lightweight agent to verify security postures of employee-owned devices across different OS. This strategy aims to fill compliance gaps without invasive management, crucial for SMBs facing SOC 2 demands.
A lightweight device security checker for remote teams with mixed hardware is being piloted as a first-step solution to verify compliance with security standards like SOC 2. This approach, aimed at operations and security leads, seeks to address the challenge of managing employee-owned devices across different operating systems without invasive controls.
The proposed tool is a voluntary, lightweight agent that employees install on their personal devices, including MacBooks, Windows laptops, and smartphones. It checks critical security features such as disk encryption, OS updates, screen lock activation, and password manager presence. The agent reports pass/fail status to a centralized dashboard, providing teams with visibility into device security postures without remote control or intrusive management.
This solution responds to the compliance verification gap created by traditional mobile device management (MDM) systems, which are often too invasive for employee-owned devices. As companies face increasing pressure from SOC 2 audits and customer security reviews, this lightweight approach offers a scalable way to demonstrate security posture with minimal friction.
Initial deployment involves ten remote startups, with success measured by device enrollment rates and the acceptance of security reports by auditors. The tool is offered on a per-device monthly pricing model, with additional features like compliance report exports available on paid tiers.
Why Lightweight Device Checks Matter for SMBs
This approach could significantly improve security compliance for small and medium-sized businesses (SMBs) that rely on employee-owned devices. As remote work expands, ensuring these devices meet security standards becomes more complex but essential, especially with increasing regulatory scrutiny like SOC 2. The lightweight agent offers a non-invasive, scalable way to verify device security, reducing the risk of breaches and compliance violations without disrupting employee workflows.
device security compliance checker
As an affiliate, we earn on qualifying purchases.
As an affiliate, we earn on qualifying purchases.
Growing Need for Non-Invasive Security Verification in Remote Teams
Remote work has led many companies to rely heavily on personal devices for access to company data. However, traditional endpoint security solutions, such as mobile device management (MDM), often require invasive controls that employees may resist. Meanwhile, compliance standards like SOC 2 now demand detailed verification of device security postures, including encryption and update status. Currently, many companies lack a straightforward way to verify these aspects on employee-owned hardware without risking employee dissatisfaction or privacy concerns.
Recent market trends show a rising demand for lightweight, voluntary security tools that can quickly assess device health and compliance. Pilot programs are emerging to test such solutions, focusing on SMBs that face the dual challenge of limited resources and strict compliance requirements. The concept of a simple agent that reports security status without remote control is gaining traction as a practical compromise.
lightweight security agent for laptops
As an affiliate, we earn on qualifying purchases.
As an affiliate, we earn on qualifying purchases.
Unanswered Questions About Deployment and Auditor Acceptance
It remains unclear how quickly companies will adopt this approach at scale and whether auditors will accept these security reports as sufficient evidence for compliance. The effectiveness of the agent across diverse device configurations and OS versions also needs further validation. Additionally, questions about long-term maintenance, employee privacy concerns, and integration with existing security workflows are still being explored.
mobile device security verification tool
As an affiliate, we earn on qualifying purchases.
As an affiliate, we earn on qualifying purchases.
Next Steps for Pilot Deployment and Validation
The initial deployment at ten startups will provide data on device enrollment rates, user acceptance, and audit acceptance of the reports. Success metrics include high enrollment, consistent reporting, and positive feedback from auditors. Based on these results, the solution could expand to more organizations, with further refinements in reporting features and integration options. Ongoing discussions with security standards bodies may also influence future validation criteria for such lightweight tools.
remote device security monitoring software
As an affiliate, we earn on qualifying purchases.
As an affiliate, we earn on qualifying purchases.
Key Questions
How does the lightweight agent improve device security?
The agent checks key security features like disk encryption, OS updates, screen lock activation, and password manager presence, providing a quick security posture report.
Will employees be resistant to installing this agent?
Since the agent is voluntary and designed to be minimally invasive, employee resistance is expected to be low, especially if it helps with compliance without remote control features.
Can this approach replace traditional MDM solutions?
It is intended as a supplement or initial verification step, not a complete replacement, particularly for managing company-owned devices. It targets compliance verification for employee-owned hardware.
Will auditors accept reports from this lightweight tool?
This is still under evaluation; initial pilot results will inform whether the reports meet compliance standards and are accepted by auditors.
What are the privacy implications for employees?
The tool only reports security posture data and does not enable remote control, aiming to respect employee privacy while providing security verification.
Source: IdeaNavigator AI
Fall yard work Picks
leaf blowers
As an affiliate, we earn on qualifying purchases.