📊 Full opportunity report: Cybersecurity operations signal monitor: A backdoor in a LinkedIn job offer on IdeaNavigator AI — validation score, market gap, and execution plan.

Get hardware and tech essentials delivered free — and shop member deals
- Fast, free delivery on millions of items
- Access to Prime Big Deal Days deals on October 6–7
- Prime Video, Amazon Music and more included
TL;DR
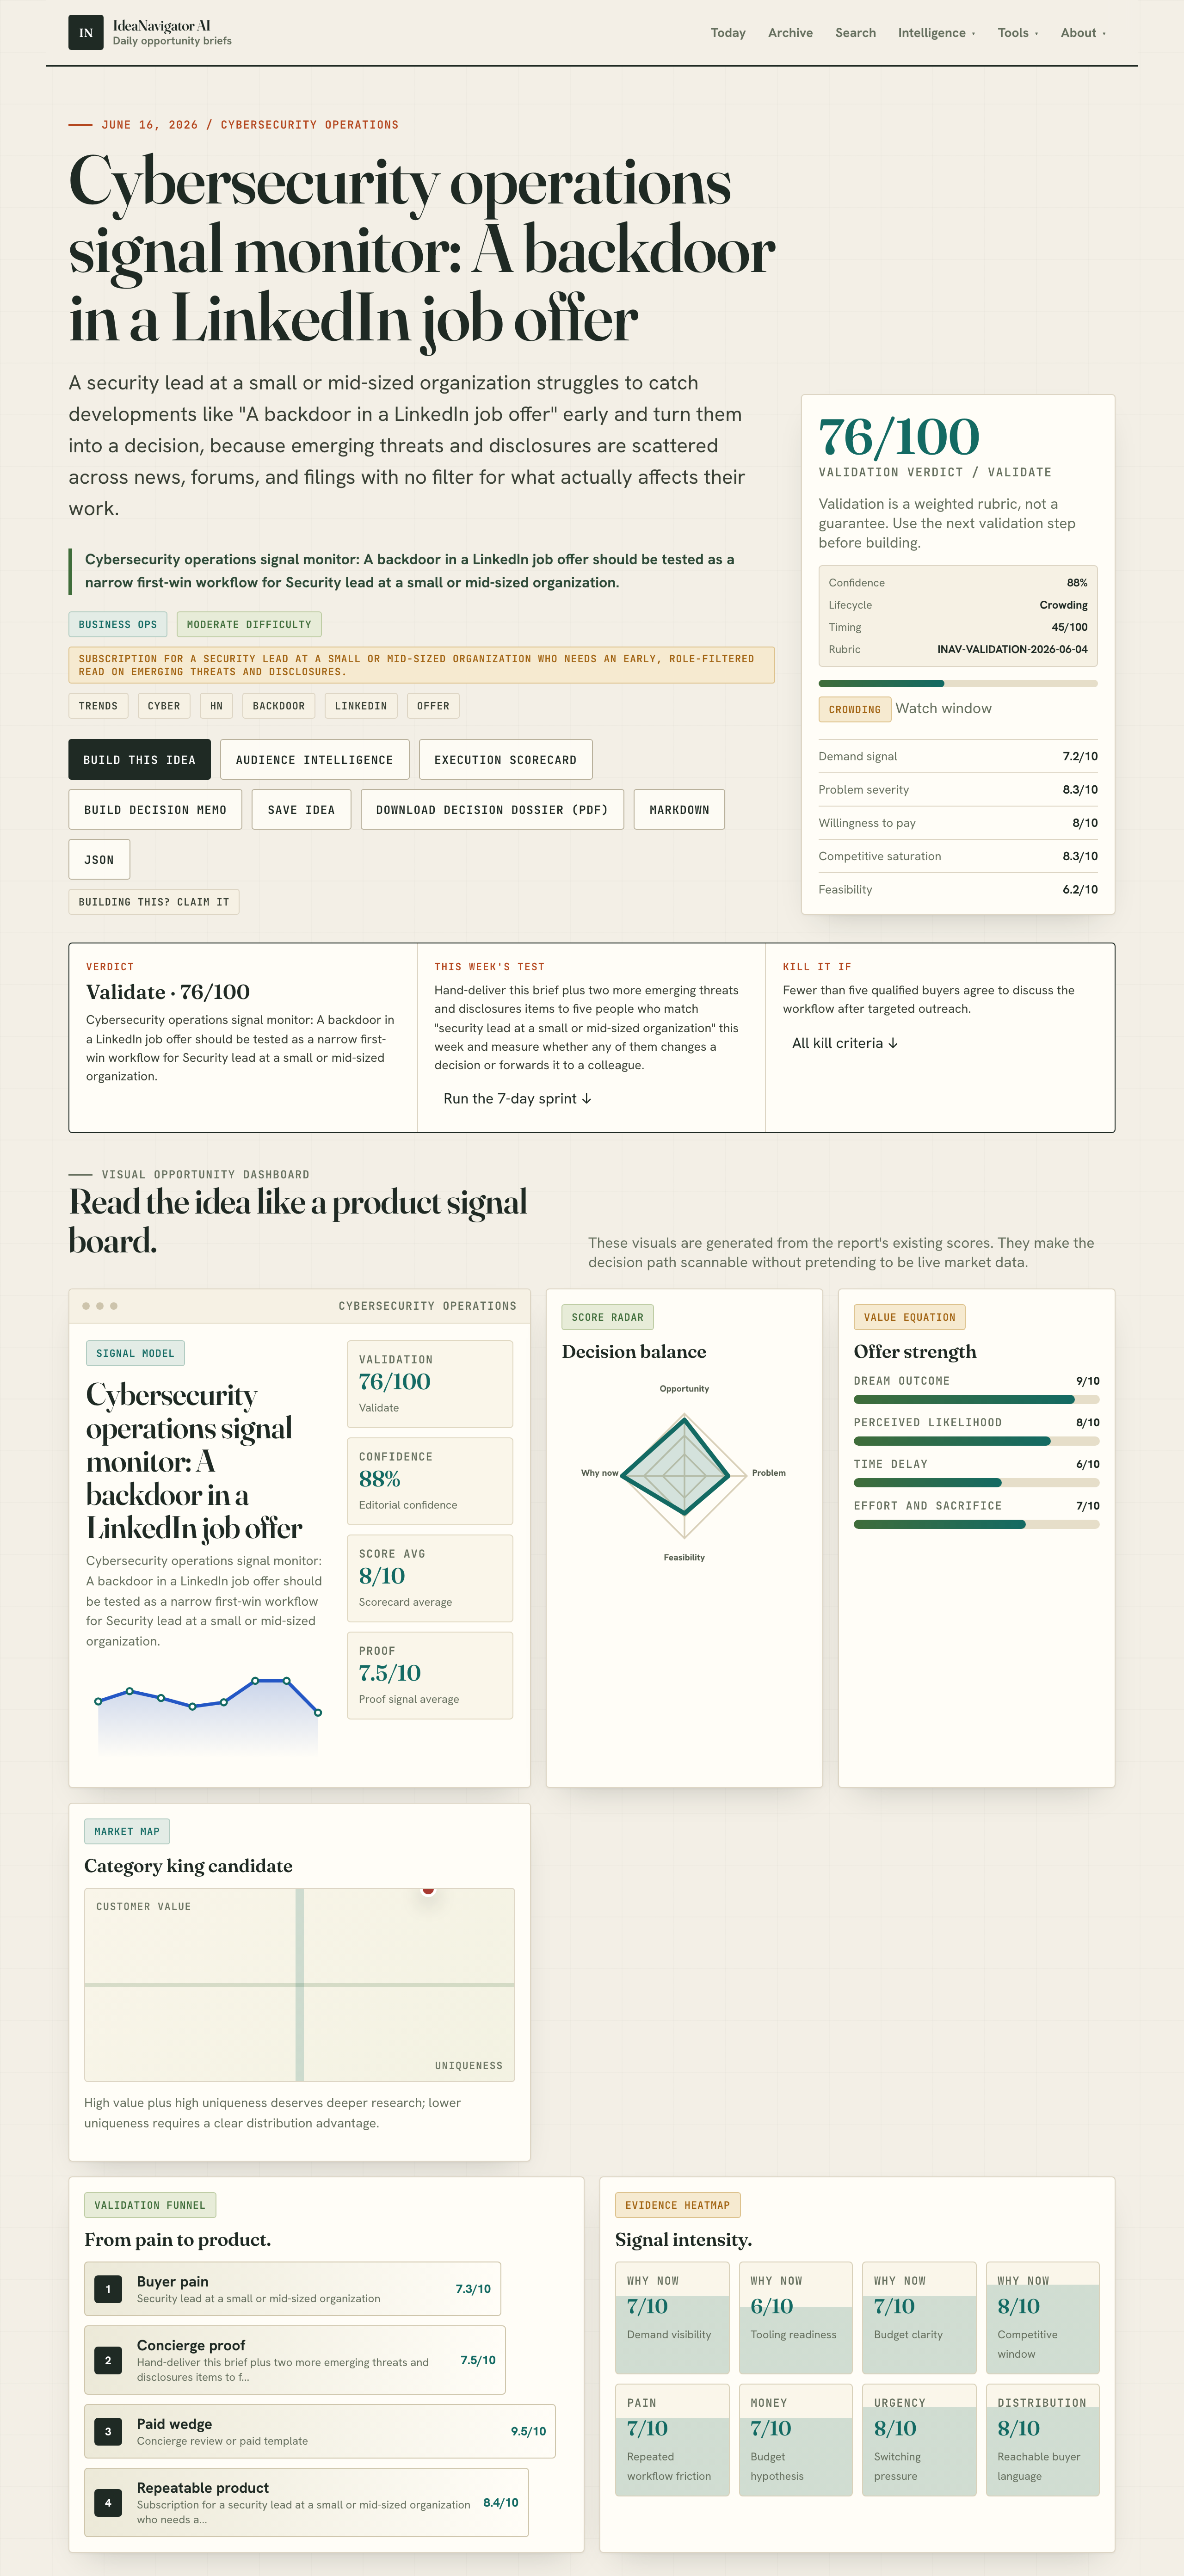
Cybersecurity analysts have identified a backdoor embedded in a LinkedIn job posting, highlighting emerging threats. The discovery is confirmed and under investigation, with potential implications for organizational security.
Cybersecurity analysts have confirmed the detection of a backdoor embedded within a LinkedIn job offer, marking a significant development in targeted cyber threats. The discovery was made as part of ongoing monitoring efforts and is now under investigation by security authorities.
The confirmed incident involves a malicious backdoor inserted into a LinkedIn job posting, which could potentially be exploited by hackers to gain unauthorized access to corporate networks. The detection was made through cybersecurity operations signal monitoring, which flagged unusual activity associated with the posting. Experts emphasize that such backdoors in social media job offers are increasingly used as vectors for targeted attacks against organizations, especially small and mid-sized firms lacking advanced security measures.At this stage, authorities have not disclosed the specific technical details of the backdoor or whether it has been exploited in active campaigns. The LinkedIn post has been removed, and cybersecurity teams are analyzing the incident to assess the scope of potential damage and mitigation steps.Potential Impact on Small and Mid-Sized Organizations
This discovery underscores the growing sophistication of cyber threats targeting social media platforms used for recruitment. For small and mid-sized organizations, which often lack dedicated cybersecurity resources, such backdoors pose a serious risk of data breaches and network infiltration. The incident highlights the importance of vigilant monitoring of social media and job postings for signs of malicious activity, as well as the need for stronger security protocols to prevent exploitation of such vulnerabilities.Furthermore, the incident demonstrates how cyber adversaries are increasingly using social engineering and platform-specific tactics to bypass traditional defenses, making awareness and proactive monitoring essential for organizational security resilience.As an affiliate, we earn on qualifying purchases.
Recent years have seen a rise in cyber threats exploiting social media platforms for malicious purposes, including spear-phishing, malware distribution, and backdoor access. In particular, hackers have targeted job offers on platforms like LinkedIn to embed malicious code or links, aiming to compromise the networks of organizations that respond to these postings. This approach leverages the trust and widespread use of social media for professional recruitment, making it a fertile ground for targeted attacks.Previously, cybersecurity firms have reported similar incidents involving malicious job postings, but confirmed backdoors embedded directly in offers remain a relatively new development. The current detection aligns with broader trends emphasizing the need for enhanced social media security awareness among security professionals.
“Organizations should treat social media posts, especially job offers, with the same caution as email attachments or links from unknown sources.”
— a cybersecurity researcher
As an affiliate, we earn on qualifying purchases.
Details of the Backdoor Exploitation Still Unclear
It is not yet confirmed whether the backdoor has been actively exploited or remains dormant. The specific technical details of the backdoor, such as its mechanism of operation or targeted systems, have not been publicly disclosed. Authorities and cybersecurity teams are still analyzing the incident, and further information is expected as investigations progress.
network intrusion detection system
As an affiliate, we earn on qualifying purchases.
As an affiliate, we earn on qualifying purchases.
Ongoing Investigation and Security Recommendations
Cybersecurity teams are continuing to analyze the incident to determine the scope and potential impact. Organizations are advised to review their social media monitoring protocols, especially concerning recruitment postings, and to implement enhanced security measures such as multi-factor authentication and network segmentation. Further updates from authorities are anticipated as the investigation unfolds.
As an affiliate, we earn on qualifying purchases.
Key Questions
How common are backdoors in social media job offers?
While increasingly reported, backdoors embedded in social media job postings are still relatively rare but growing as a tactic among cyber adversaries targeting organizations.
What should organizations do if they encounter a suspicious job offer?
Organizations should verify the legitimacy of the posting, avoid clicking on unknown links, and report suspicious activity to cybersecurity authorities for further analysis.
Can this backdoor be exploited remotely?
It is not yet confirmed whether the backdoor is actively exploited or how it functions. Ongoing investigations aim to clarify these details.
What are the immediate security measures to prevent such threats?
Organizations should implement social media monitoring, educate staff on social engineering risks, and strengthen overall cybersecurity defenses, including endpoint security and access controls.
Source: IdeaNavigator AI
Fall Picks
fall essentials
As an affiliate, we earn on qualifying purchases.